
- Home
- »
- IT Services & Applications
- »
-
Vendor Risk Management Market Size Report, 2026-2033GVR Report cover

Vendor Risk Management Market (2026 - 2033)
Size, Share, & Trends Analysis Report By Solution (Financial Control, Compliance Management), By Deployment (Cloud, On-premise), By Enterprise Size (SMEs, Large Enterprises), By End-use, By Region, And Segment Forecasts
Market Size, 2025
$12.3BMarket Estimate, 2026
$14.2BMarket Forecast, 2033
$38.1BCAGR, 2026–2033
15.2%Vendor Risk Management Market Summary
The global vendor risk management market size was valued at USD 12.3 billion in 2025 and is projected to grow from USD 14.2 billion in 2026 to USD 38.1 billion by 2033, at a CAGR of 15.2% from 2026 to 2033. North America dominated the market, accounting for a revenue share of 59.0% in 2025. This growth is driven by stringent cybersecurity regulations, increasing third-party cyber risks, and widespread adoption of cloud-based enterprise risk management solutions.
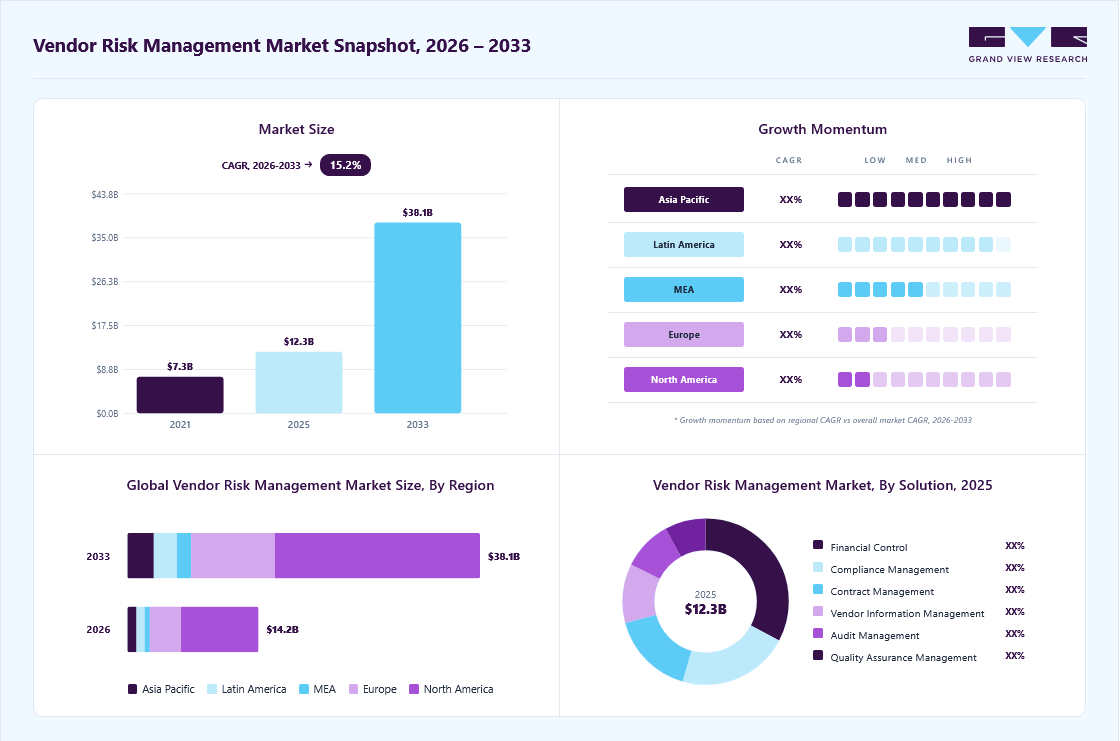 Source: Grand View Research, IR Documents, Primary Interviews, Paid DatabasesTo learn more about this report,
 Download Free Sample Report
Key Market Trends & Insights
- By solution: Financial control segment led the market and accounted for a share of 32.7% in 2025.
- By deployment: On-premise segment dominated the market, with a revenue share of 65.7% in 2025.
- By enterprise size: SMEs segment dominated the market, with a revenue share of 68.8% in 2025.
- By end use: BFSI segment held the largest revenue share in 2025.
Regional Highlights
- Largest regional market: North America (59.0% revenue share, 2025)
- Fastest-growing regional market: Asia Pacific (highest CAGR, 2026-2033)
- By country: The U.S. held the largest market share in 2025.
Market Size & Forecast
- Market size in 2025: USD 12.3 Billion
- Estimated market size in 2026: USD 14.2 Billion
- Projected market size by 2033: USD 38.1 Billion
- CAGR (2026-2033): 15.2%
Three ways to get this report
Buy it, customize it, or ask a question.Ask an Analyst
Analyst response in 1 business day
- AccessReport author, directly
- Reply timeWithin 1 working day
- No sales callDirect answer only
- FormatEmail reply
- CostFree, no cost
Get the Full Report
What the study covers
- FormatsPDF · Excel · Dashboard
- Timeline2026–2033 annual, 2025 base
- Coverage20+ countries, 5 regions
- Companies10+ key players profiled
Customize the Report
20% free customization
- IncludeCountries, segments, points
- TailorTo your product definition
- ExtendDeeper competitor detail
- OrA fully bespoke study
- Turnaround5–10 working days
The growth of the vendor risk management (VRM) industry can be attributed to the increasing reliance on third-party vendors across industries. Organizations are outsourcing critical functions to third-party suppliers, exposing them to potential risks such as data breaches, regulatory non-compliance, and reputational damage. As a result, the need for robust VRM solutions to assess, monitor, and mitigate these risks has become essential.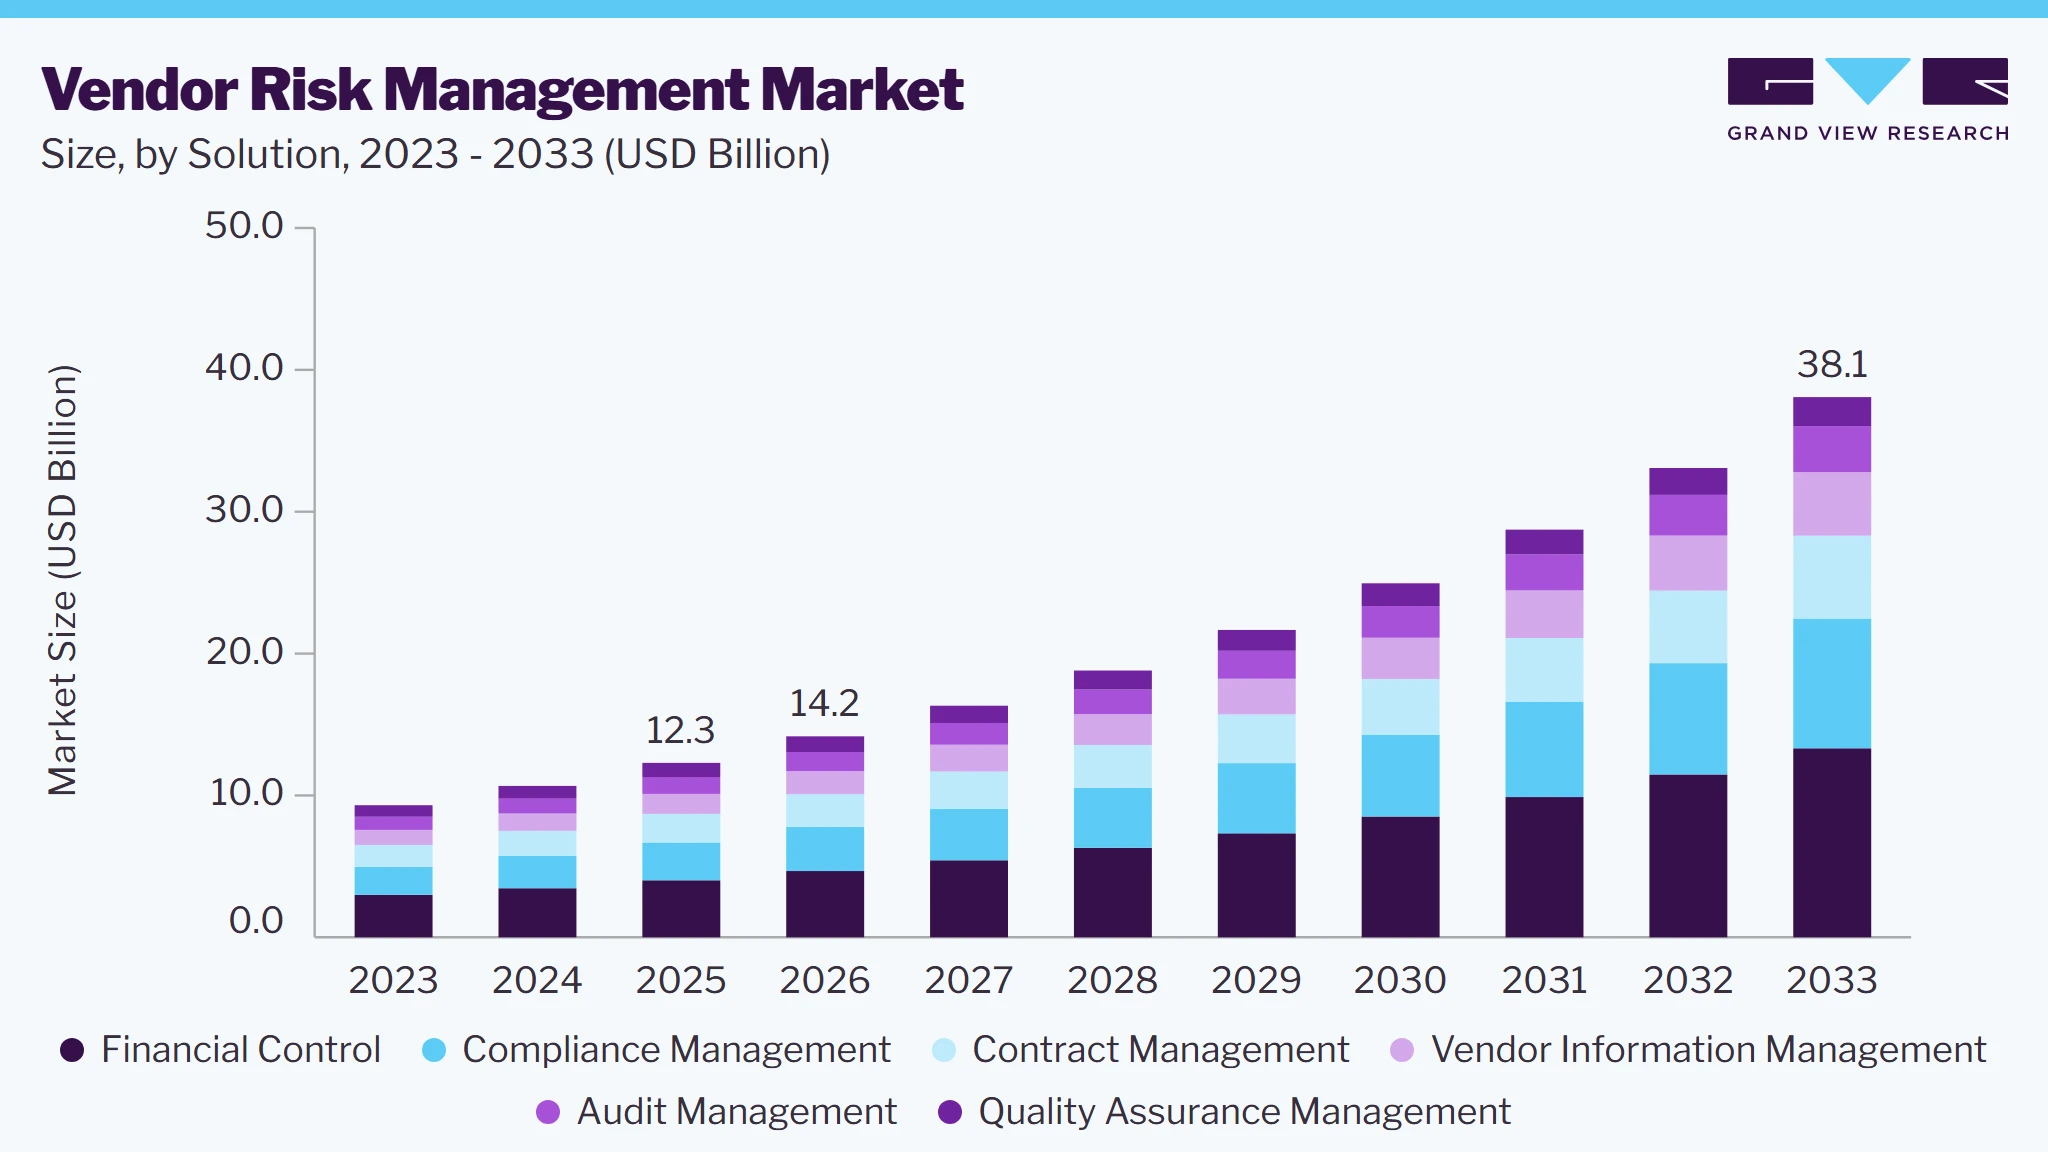 To learn more about this report, Download Free Sample Report
The rise in cyber threats and data breaches has heightened the focus on vendor cybersecurity. Companies are investing in VRM tools to evaluate the security postures of their vendors, ensuring sensitive data is protected throughout the supply chain. Cloud-based VRM platforms, in particular, are gaining traction due to their scalability, cost-efficiency, and real-time monitoring capabilities. According to a U.S.-based telecommunication company, Verizon's "2024 Data Breach Investigations Report," there was a significant 180% increase in the use of vulnerabilities to trigger data breaches in 2023 compared to 2022. Among these breaches, 15% were linked to third parties or suppliers, which include software supply chains, hosting partners, or data custodians.
The growing complexity of global supply chains also fuels vendor risk management industry expansion. Organizations with geographically dispersed vendors face increased risks related to geopolitical issues, economic instability, and supply chain disruptions. Advanced VRM solutions enable businesses to gain deeper insights into their vendors’ performance, compliance levels, and risk profiles, allowing proactive management of potential disruptions.
Regulatory compliance is another significant driver in the vendor risk management industry. Governments and regulatory bodies worldwide are enforcing stricter compliance requirements, such as the General Data Protection Regulation (GDPR), California Consumer Privacy Act (CCPA), and other industry-specific standards. These regulations mandate organizations to maintain accountability for their vendors’ practices, further emphasizing the importance of implementing effective VRM systems.
Market Dynamics
The global vendor risk management market is experiencing strong growth as organizations increasingly strengthen third-party risk oversight amid expanding digital ecosystems, globalized supply chains, and evolving cybersecurity threats. Enterprises across banking, healthcare, manufacturing, retail, IT & telecommunications, government, energy, and life sciences are adopting vendor risk management platforms to assess supplier risks, automate due diligence, monitor regulatory compliance, evaluate cybersecurity posture, and ensure business continuity. Modern VRM solutions incorporate artificial intelligence (AI), machine learning (ML), continuous risk monitoring, security ratings, workflow automation, contract lifecycle integration, and predictive analytics to help organizations proactively identify and mitigate risks associated with third-party vendors, fourth-party dependencies, and outsourced services across hybrid and cloud-based business environments.
The growing frequency of third-party cyberattacks and the tightening of regulatory requirements are major drivers of the global vendor risk management market. Organizations are increasingly relying on external vendors for cloud services, software development, logistics, payment processing, and business operations, significantly expanding their third-party risk exposure. Vendor risk management platforms enable enterprises to automate vendor onboarding, security assessments, continuous monitoring, regulatory compliance, due diligence, and remediation workflows while improving visibility across complex supplier ecosystems. AI-powered VRM solutions further enhance risk identification by continuously monitoring vendor security posture, financial stability, operational resilience, and compliance with evolving regulations. For instance, in March 2026, ProcessUnity launched the ProcessUnity Risk Index, a controls-driven vendor risk rating solution that combines internal control intelligence with external threat and vulnerability data to continuously assess third-party risk. The solution helps organizations automate vendor risk assessments, prioritize remediation efforts, strengthen cybersecurity oversight, and improve compliance across increasingly complex third-party ecosystems.
The increasing complexity of global vendor ecosystems and the cost of implementing enterprise-wide vendor risk management programs remain significant restraints for the global VRM market. Large organizations often manage thousands of third-party relationships across multiple regions, requiring integration with procurement, governance, risk and compliance (GRC), ERP, cybersecurity, and identity management systems. These integrations increase deployment complexity, implementation time, and total cost of ownership. Additionally, maintaining accurate vendor inventories, conducting periodic reassessments, collecting risk evidence, and responding to evolving regulatory requirements require dedicated personnel and ongoing operational investments. Small and medium-sized enterprises (SMEs) may face budget limitations, resource constraints, and insufficient risk management expertise, slowing adoption of comprehensive VRM platforms.
The increasing adoption of AI, predictive analytics, and continuous monitoring technologies presents significant growth opportunities for the global vendor risk management market. Organizations are moving beyond periodic vendor assessments toward real-time risk intelligence that continuously evaluates cybersecurity posture, financial health, operational resilience, ESG performance, and regulatory compliance across third- and fourth-party networks. Growing investments in cloud computing, digital supply chains, zero-trust security frameworks, and integrated governance, risk, and compliance (GRC) programs are driving demand for intelligent VRM platforms capable of automating risk scoring, evidence collection, regulatory reporting, and remediation workflows. As enterprises seek greater visibility into interconnected vendor ecosystems while improving resilience against cyber threats and operational disruptions, AI-enabled vendor risk management solutions are expected to witness substantial adoption across industries.
Analyst Perspective
The vendor risk management market is positioned at the intersection of expanding third-party ecosystems, increasing cybersecurity threats, evolving regulatory requirements, and accelerating enterprise digital transformation. Organizations across BFSI, healthcare, manufacturing, retail, IT and telecommunications, government, energy and utilities, and other industries are increasingly deploying vendor risk management solutions to strengthen third-party governance, improve operational resilience, and ensure regulatory compliance. Unlike traditional spreadsheet-based or manual vendor assessment processes, modern vendor risk management platforms provide centralized vendor lifecycle management, automated due diligence, continuous risk monitoring, cybersecurity assessments, compliance tracking, contract oversight, and audit management. Moreover, advanced platforms increasingly leverage AI, predictive analytics, and real-time risk monitoring to automate vendor assessments, strengthen compliance, and reduce cybersecurity and operational risks.
Solution Insights
Based on solution, the financial control segment led the market with the largest revenue share of 32.7% in 2025. When selecting vendors, organizations need to perform due diligence to ensure that the chosen third-party partners are financially sound and capable of meeting contractual obligations. The due diligence process includes assessing the financial health, creditworthiness, and operational stability of potential vendors. Financial risks associated with vendors can lead to significant losses, both in terms of the business’s bottom line and reputation.
The compliance management segment is expected to grow to a significant CAGR of 16.7% over the forecast period. VRM compliance management solutions are increasingly being integrated into broader Enterprise Risk Management (ERM) frameworks. This integration ensures that compliance is managed in tandem with other risk factors and provides a more comprehensive view of the risks posed by vendors. By integrating these systems, businesses can identify compliance risks earlier, reduce the likelihood of costly compliance violations, and improve overall risk mitigation efforts.
Deployment Insights
Based on deployment, the on-premise segment led the market with the largest revenue share of 65.7% in 2025. Despite the rise of cloud computing, many businesses still maintain on-premises environments due to specific regulatory, security, or operational requirements. As a result, managing vendor risks related to on-premises solutions remains crucial, especially in highly regulated industries and in organizations with legacy systems.
The cloud segment is expected to grow at a significant CAGR over the forecast period. The global shift towards digital transformation is a primary driver of the growing need for VRM solutions in the cloud segment. As organizations across industries such as finance, healthcare, retail, and manufacturing adopt cloud-based platforms and Software-as-a-Service (SaaS) solutions, they become increasingly dependent on third-party cloud service providers.
Enterprise Size Insights
Based on enterprise size, the SMEs segment led the market with the largest revenue share of 68.8% in 2025. With the advent of more affordable VRM tools and solutions tailored for SMEs, organizations are increasingly able to manage their vendor-related risks without straining their budgets. Many VRM vendors now offer cloud-based and SaaS solutions that are scalable and cost-effective for smaller organizations.
The large enterprise segment is expected to grow at a significant CAGR over the forecast period. Large enterprises often rely on multiple vendors for critical services, making business continuity and disaster recovery plans an essential part of risk management. A disruption in a key vendor’s operations can have a ripple effect on the enterprise’s ability to deliver products and services to customers. This risk is particularly significant for large enterprises with global operations or those who rely on just-in-time inventory or logistics.
End-use Insights
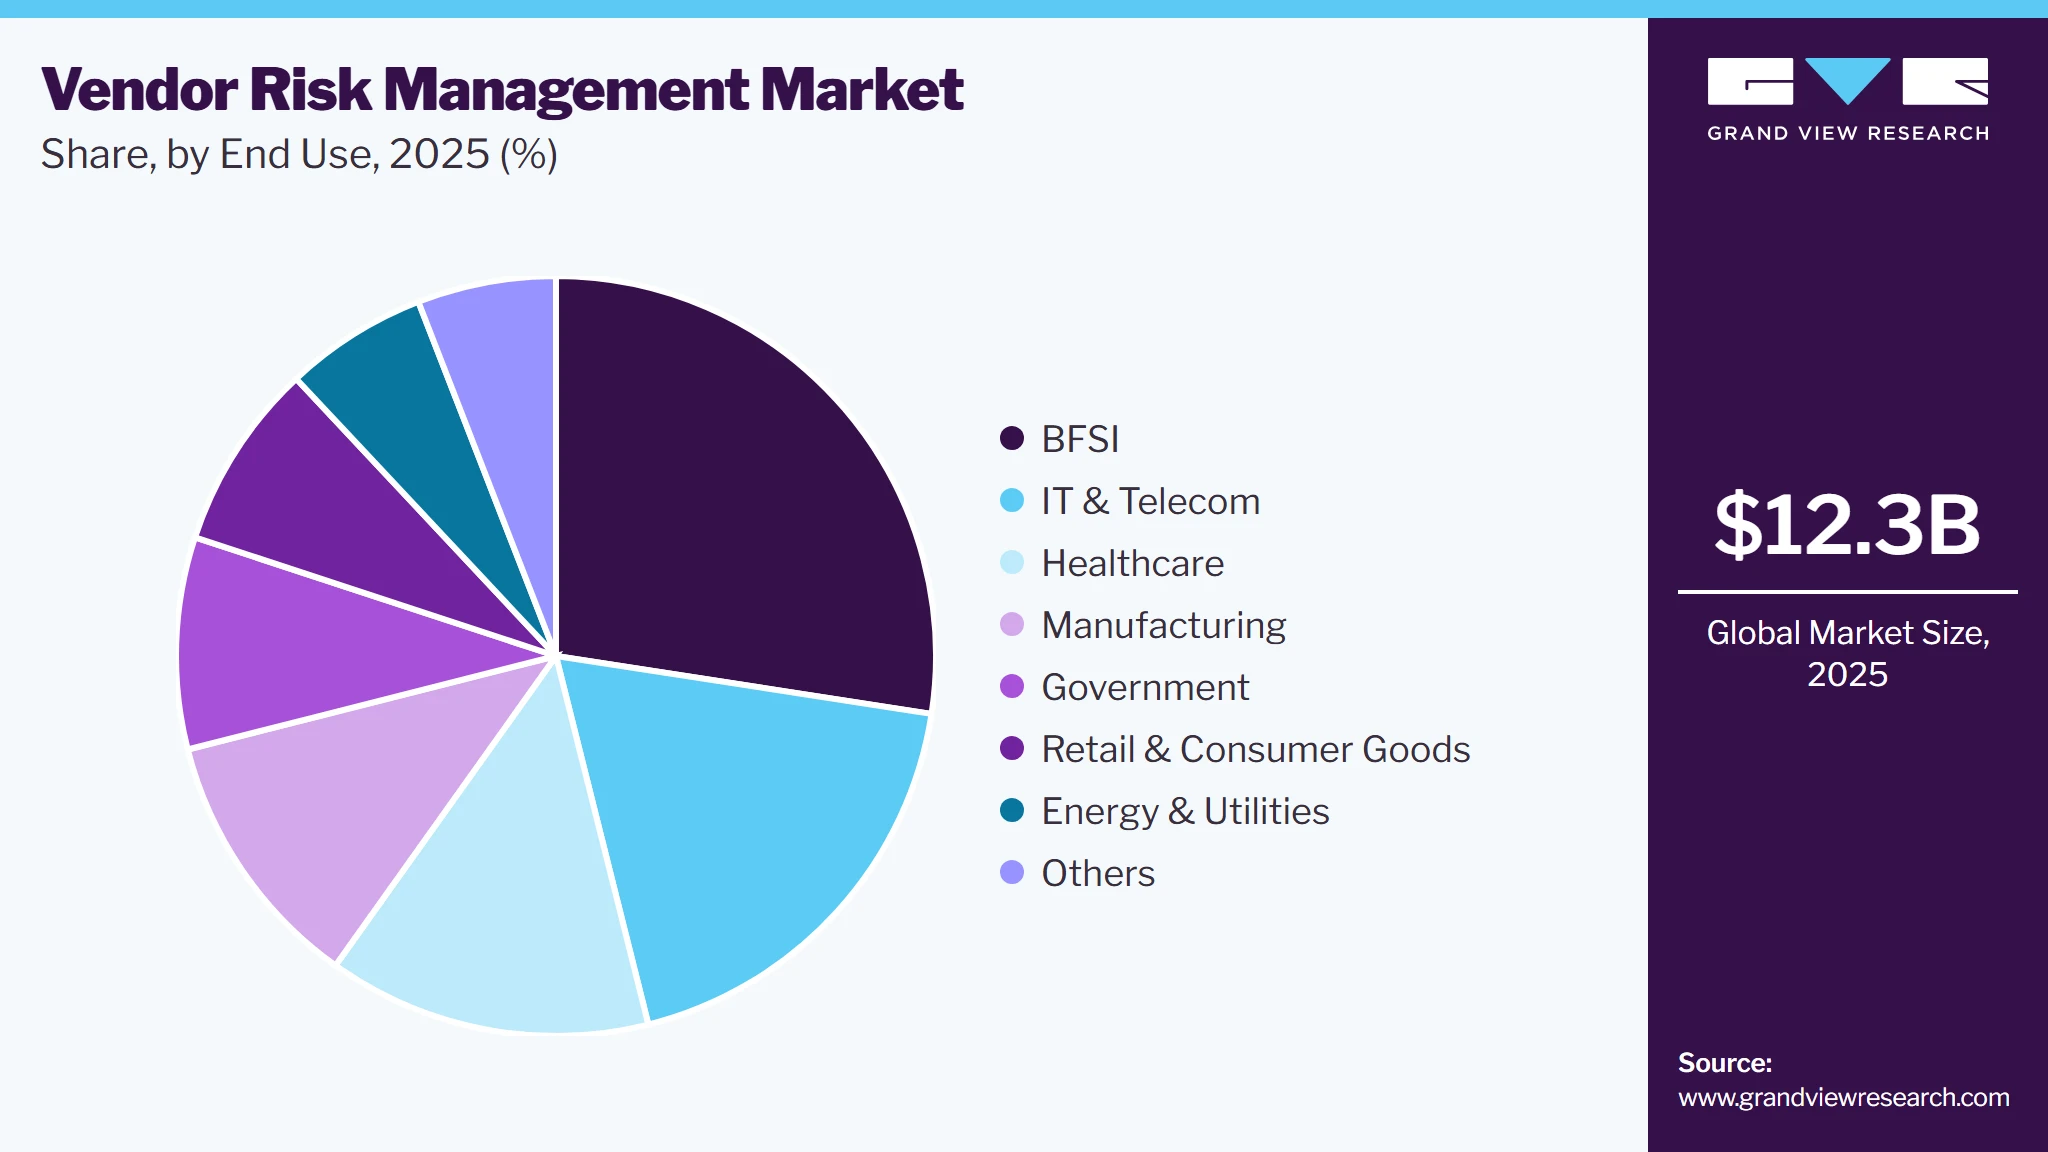
Based on end use, BFSI segment led the market with the largest revenue share of 27.4% in 2025. Digital transformation initiatives are driving growth in the VRM market for the BFSI segment. The adoption of technologies like AI, blockchain, and IoT increases the complexity of vendor ecosystems, necessitating sophisticated VRM systems. These tools leverage analytics and machine learning to assess risks proactively and streamline vendor lifecycle management.
 To learn more about this report, Download Free Sample Report
The healthcare segment is expected to grow at a significant CAGR over the forecast period. The adoption of advanced technologies, including telemedicine, electronic health records (EHRs), and cloud-based healthcare platforms, has significantly expanded the reliance on third-party vendors. These technologies, while enhancing operational efficiency, have also increased the complexity of vendor ecosystems and exposed healthcare organizations to potential risks such as data breaches and operational disruptions. VRM tools play a pivotal role in mitigating these risks by providing real-time visibility into vendor operations and ensuring alignment with security and performance standards.
Regional Insights
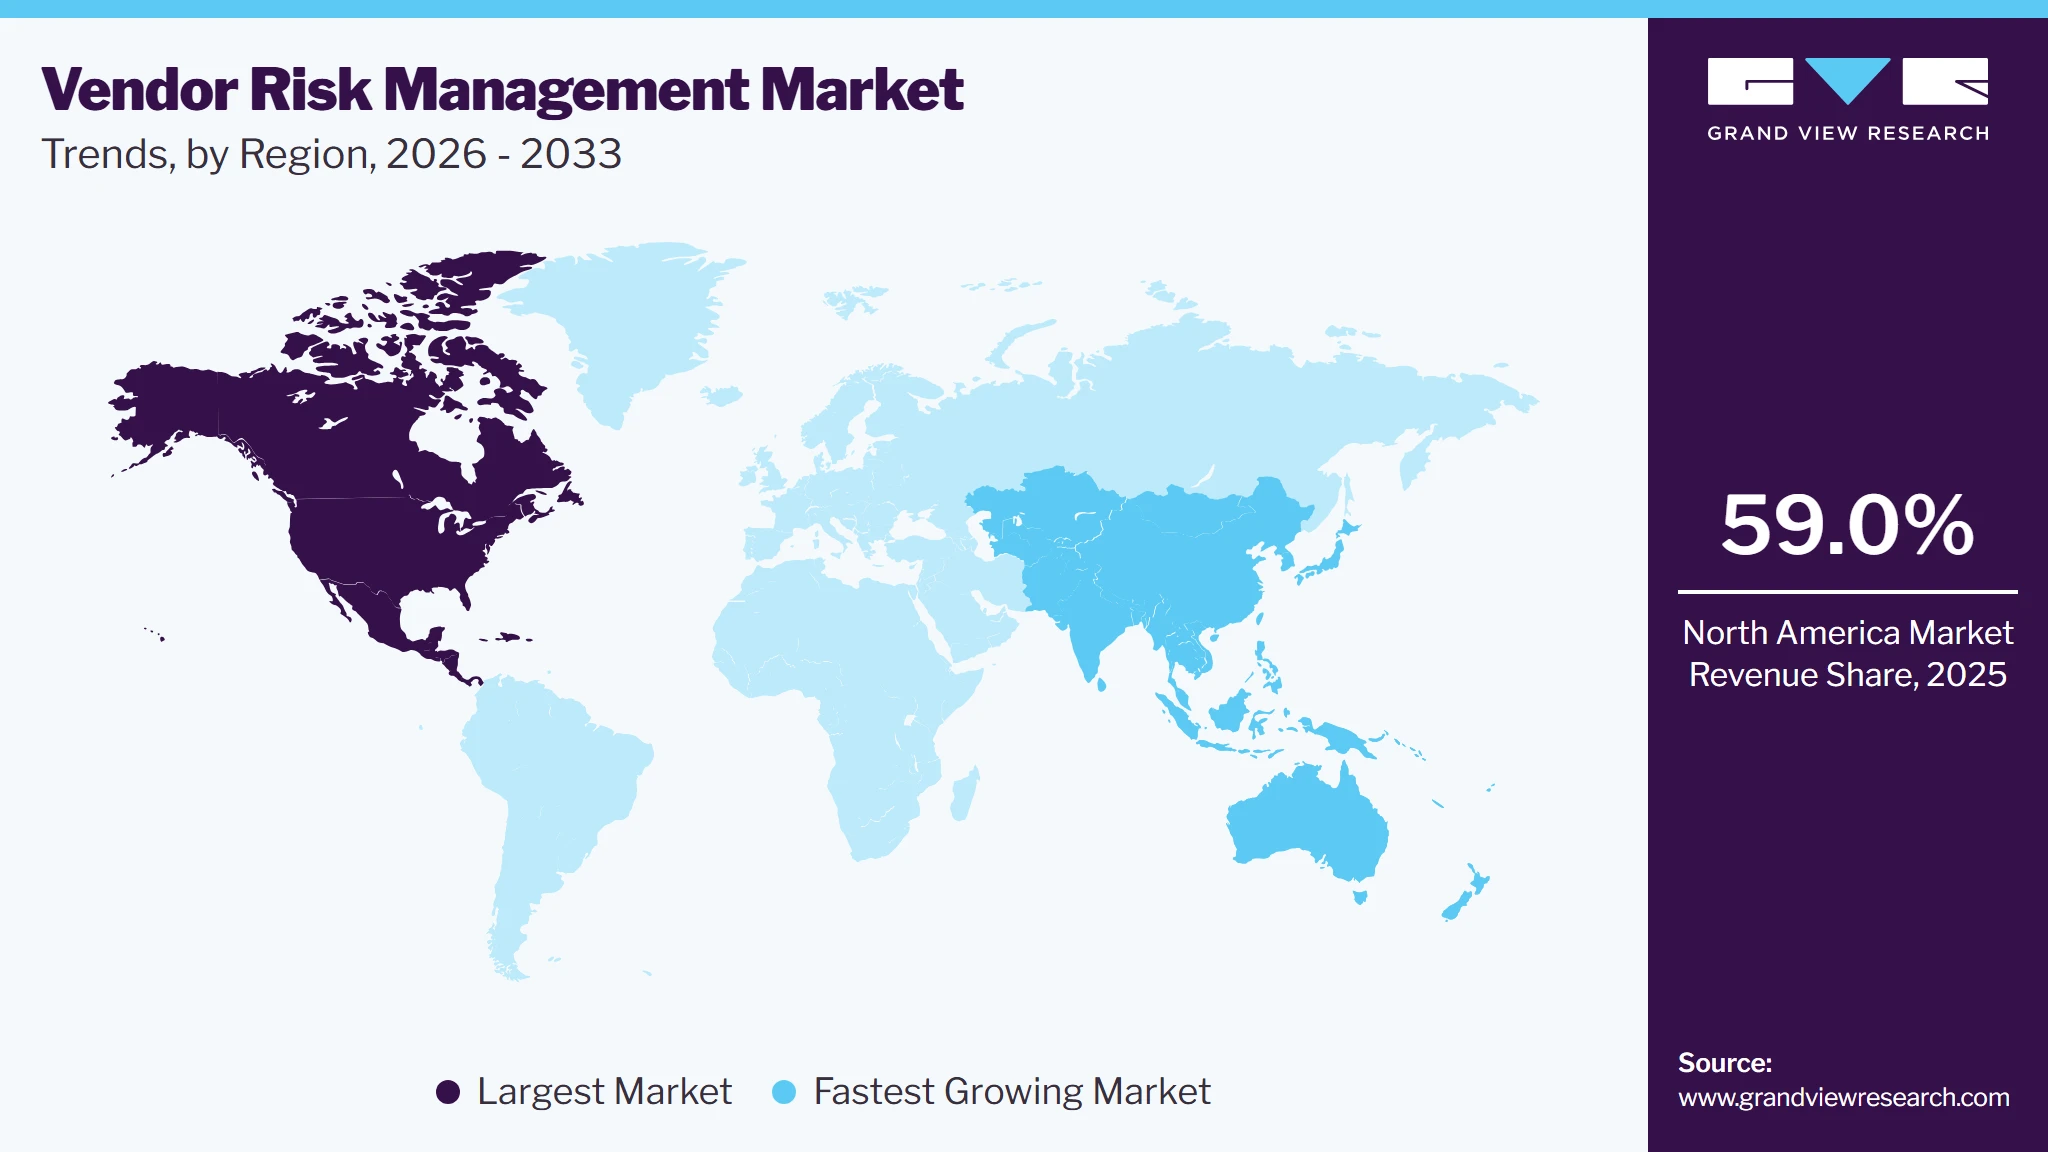
North America dominated the global vendor risk management market with the largest revenue share of 59.0% in 2025. The digital transformation and adoption of cloud technologies are also fueling growth in the VRM market in North America. As businesses migrate to cloud-based environments, they are more reliant on third-party service providers, raising concerns about data privacy, uptime, and service reliability. Cloud-based VRM platforms offer organizations scalability, cost-efficiency, and real-time monitoring capabilities, which are essential for managing and mitigating risks associated with cloud vendors.
 To learn more about this report, Download Free Sample Report
U.S. Vendor Risk Management Industry Trends
The vendor risk management market in the U.S. held the largest share in the North America region in 2025. Federal and state-level regulations, such as the Gramm-Leach-Bliley Act (GLBA), Sarbanes-Oxley Act (SOX), and California Consumer Privacy Act (CCPA), are pushing U.S. companies to ensure that their vendors comply with strict data protection, privacy, and financial regulations. The Federal Financial Institutions Examination Council (FFIEC) also mandates financial institutions to assess and manage third-party risks to protect consumers' financial data. The ever-expanding regulatory frameworks necessitate continuous monitoring and assessment of vendor performance, a task VRM platforms are well equipped to handle.
Europe Vendor Risk Management Industry Trends
The vendor risk management market in Europe is anticipated to register considerable growth from 2026 to 2033. The increasing awareness among European businesses about the financial and reputational risks associated with vendor failures is driving VRM adoption. Companies understand that poor vendor performance, non-compliance, or a cyber breach originating from a third-party vendor can lead to significant financial losses, legal issues, and reputational damage. As a result, businesses across Europe are investing in VRM solutions that allow them to proactively identify and mitigate risks, improve vendor relationships, and ensure continuity in their supply chains.
UK Vendor Risk Management Industry Trends
The UK vendor risk management market is expected to grow rapidly in the coming years. The growth of the gig economy in the UK has introduced new types of vendors and third-party providers, such as freelancers, contractors, and digital platforms. These vendors often operate with different risk profiles compared to traditional suppliers, and their relationships with organizations can be harder to manage. As businesses increasingly rely on gig workers and freelancers, the need for specialized VRM solutions to assess the risks associated with these types of vendors particularly for compliance, data security, and quality assurance has risen.
Germany Vendor Risk Management Industry Trends
The Germany vendor risk management market held a substantial market share in 2025, owing to growth in the automotive and industrial sectors. Germany is highly dependent on complex, multinational supply chains. The reliance on suppliers and subcontractors across various geographies introduces risks related to political instability, economic changes, and natural disasters.
Asia Pacific Vendor Risk Management Industry Trends
The vendor risk management industry in the Asia Pacific is anticipated to grow at the fastest CAGR from 2026 to 2033. The region is undergoing significant digital transformation, with a large number of businesses shifting to cloud-based platforms and services. Countries such as Australia, and Japan are at the forefront of this digital shift, with organizations increasingly relying on cloud service providers, SaaS platforms, and IT outsourcing for operational efficiency and cost savings. While cloud adoption offers many benefits, it also introduces new risks associated with data security, vendor lock-in, and compliance.
Japan Vendor Risk Management Industry Trends
The Japan vendor risk management market is expected to grow rapidly in the coming years. As Environmental, Social, and Governance (ESG) factors gain importance globally, Japanese companies are under increasing pressure from investors, consumers, and regulators to adopt more responsible and sustainable practices. Japan has also committed to achieving net-zero emissions by 2050 and is implementing ESG frameworks in corporate governance, which extends to third-party vendors. Organizations in Japan are adopting VRM tools to assess the ESG performance of their vendors, ensuring that suppliers align with environmental sustainability, social responsibility, and good governance practices
China Vendor Risk Management Industry Trends
The China vendor risk management market held a substantial market share in 2025. China’s rapid technological innovation is impacting the VRM market, with new solutions emerging to meet the growing need for managing vendor risks. Companies are increasingly turning to advanced blockchain technology, big data analytics, and IoT-based solutions to track vendor performance and ensure supply chain transparency. These technologies help businesses gather real-time data on vendor activities, assess risk factors, and make informed decisions regarding their supplier relationships.
Key Vendor Risk Management Company Insights
Key players operating in the vendor risk management industry areBitSight Technologies, Genpact, NAVEX Global, Inc.,and Prevalent, Inc. Companies are focusing on various strategic initiatives, including new product development, partnerships & collaborations, and agreements to gain a competitive advantage over their rivals. The following are some instances of such initiatives.
-
In December 2024, NAVEX Global, Inc. announced a major update to NAVEX One Compliance Assistant, which includes microlearning suggestions tailored to the specific needs of individual employees. This enhancement provides employees with real-time, relevant information about company policies and procedures. The update streamlines the compliance process by allowing employees to access information more personalized and intuitively, and encourages more accessible and self-driven compliance in organizations.
-
In August 2024, Genpact announced plans to strengthen its strategic partnership with Advantage Solutions, a U.S.-based provider of business solutions for consumer goods companies and retailers. This expanded collaboration aims to address challenges in finance and supply chain management within the consumer-packaged goods (CPG) and retail industries. The partnership aims to improve order-to-cash processes and supply chain management by addressing issues such as deduction leakage, ineffective claim recovery, manual customer service, and inefficient planning, logistics, and fulfillment.
Key Vendor Risk Management Companies:
The following key companies have been profiled for this study on the vendor risk management market.
-
BitSight Technologies
-
Genpact
-
LogicGate
-
MetricStream, Inc.
-
NAVEX Global, Inc.
-
Prevalent, Inc.
-
ProcessUnity
-
Quantivate, LLC
-
SAI Global
-
ServiceNow
Competitive Benchmarking
Category
Operating Strategies
Competitive Edge
Weakness
Established Players (BitSight Technologies, Genpact, MetricStream, Inc., NAVEX Global, Inc., SAI Global, ServiceNow)
- Established players focus on delivering comprehensive vendor risk management platforms that integrate vendor onboarding, due diligence, continuous risk monitoring, cybersecurity assessments, financial risk evaluation, compliance management, contract management, audit management, and third-party governance.
- Their strategies emphasize AI-driven risk intelligence, continuous monitoring, cloud-native platform expansion, integration with procurement, ERP, cybersecurity, and GRC systems, and strategic partnerships to strengthen enterprise-wide third-party risk management.
- Established players benefit from extensive global customer bases, mature technology platforms, significant R&D investments, broad partner ecosystems, and deep expertise in governance, risk, compliance, and cybersecurity.
- Their integrated solutions, advanced analytics, AI-powered automation, scalable SaaS offerings, and global professional services enable large enterprises to manage complex vendor ecosystems while improving operational resilience and regulatory compliance.
- These companies face challenges related to complex implementations, higher licensing and deployment costs, lengthy enterprise sales cycles, and maintaining interoperability across diverse enterprise environments.
- Continuous investment is also required to address evolving cybersecurity threats, regulatory changes, AI-driven risk analytics, and increasingly complex global supply chain risks.
Emerging Players (LogicGate, Prevalent, Inc., ProcessUnity, Quantivate, LLC)
- Emerging players focus on delivering cloud-native, flexible vendor risk management solutions that emphasize automated vendor assessments, cybersecurity risk scoring, compliance monitoring, workflow automation, and continuous third-party risk visibility.
- Their strategies prioritize rapid product innovation, AI-enabled risk analytics, competitive SaaS pricing, seamless integrations, and expansion into mid-market organizations seeking scalable vendor governance solutions.
- Emerging players offer agile product development, intuitive user interfaces, rapid implementation, flexible deployment models, and strong automation capabilities.
- Their ability to quickly introduce AI-powered risk assessments, automate vendor due diligence, and integrate with modern cloud and security ecosystems enables organizations to strengthen third-party risk management with lower implementation complexity.
- Limited global brand recognition, smaller enterprise customer bases, fewer implementation partners, and comparatively lower international presence may constrain large-scale market expansion.
- These companies also face challenges in scaling global operations, expanding channel partnerships, sustaining R&D investments, and competing with established vendors that provide broader governance, cybersecurity, and enterprise risk management platforms.
Vendor Risk Management Report Scope
Report Attribute
Details
Market size in 2025
USD 12.3 billion
Estimated market size in 2026
USD 14.2 billion
Projected market size by 2033
USD 38.1 billion
Growth rate
CAGR of 15.2% from 2026 to 2033
Base year for estimation
2025
Historical data
2021 - 2024
Forecast period
2026 - 2033
Quantitative units
Revenue in USD million/billion and CAGR from 2026 to 2033
Report coverage
Revenue forecast, company market share analysis, competitive landscape, growth factors, and trends
Segments covered
Solution, deployment, enterprise size, end use, and region
Regional scope
North America; Europe; Asia Pacific; Latin America; MEA
Country scope
U.S.; Canada; Mexico; Germany; UK; France; China; Japan; India; South Korea; Australia; Brazil; Saudi Arabia; South Africa; UAE
Key companies profiled
BitSight Technologies; Genpact; LogicGate; MetricStream, Inc.; NAVEX Global, Inc.; Prevalent, Inc.; ProcessUnity; Quantivate, LLC; SAI Global; ServiceNow
Customization scope
Free report customization (equivalent up to 8 analysts' working days) with purchase. Addition or alteration to country, regional & segment scope.
Pricing and purchase options
Avail customized purchase options to meet your exact research needs. Explore purchase options
Global Vendor Risk Management Market Report Segmentation
This report forecasts revenue growth at global, regional, and country levels and provides an analysis of the latest industry trends in each of the sub-segments from 2021 to 2033. For this study, Grand View Research has segmented the vendor risk management market report based on solution, deployment, enterprise size, end-use, and region:
-
Solution Outlook (Revenue, USD Billion, 2021 - 2033)
-
Vendor Information Management
-
Contract Management
-
Financial Control
-
Compliance Management
-
Audit Management
-
Quality Assurance Management
-
-
Deployment Outlook (Revenue, USD Billion, 2021 - 2033)
-
Cloud
-
On-premise
-
-
Enterprise Size Outlook (Revenue, USD Billion, 2021 - 2033)
-
Large Enterprises
-
Small & Medium Enterprises
-
-
End-use Outlook (Revenue, USD Billion, 2021 - 2033)
-
BFSI
-
IT & Telecom
-
Retail & Consumer Goods
-
Manufacturing
-
Energy & Utilities
-
Healthcare
-
Government
-
Others
-
-
Regional Outlook (Revenue, USD Billion, 2021 - 2033)
-
North America
-
U.S.
-
Canada
-
Mexico
-
-
Europe
-
UK
-
Germany
-
France
-
-
Asia Pacific
-
China
-
India
-
Japan
-
South Korea
-
Australia
-
-
Latin America
-
Brazil
-
-
Middle East & Africa
-
UAE
-
Saudi Arabia
-
South Africa
-
-
Research Methodology
The vendor risk management market figures in this report are based on a proven research process that combines executive interviews with secondary research from proprietary databases, company filings, and recognized regulatory and institutional sources. Market size is built through value-chain sizing - reconciling supply-side and demand-side estimates - and triangulated with bottom-up and top-down approaches. Every estimate passes multiple levels of expert validation before publication, with each vendor risk management segment quantified using the revenue-capture definitions in the table below.
Segment Definition
Segment - Solution
Revenue capture definition
Vendor Information Management
Revenue generated from software licenses, subscriptions, implementation, integration, maintenance, and support services for solutions that centralize vendor profiles, onboarding, document management, due diligence, vendor classification, and lifecycle management.
Contract Management
Revenue generated from software that automates vendor contract creation, approval, storage, renewal tracking, obligation management, and compliance throughout the contract lifecycle.
Financial Control
Revenue generated from solutions that evaluate vendor financial health, creditworthiness, payment risk, financial performance, and operational resilience through continuous monitoring and analytics.
Compliance Management
Revenue generated from software that automates vendor compliance assessments, regulatory monitoring, policy enforcement, certification tracking, security questionnaires, and remediation workflows across third-party ecosystems.
Audit Management
Revenue generated from platforms that support vendor audits, evidence collection, audit scheduling, findings management, corrective actions, reporting, and continuous third-party risk assessments.
Quality Assurance Management
Revenue generated from solutions that monitor vendor quality performance, service-level agreements (SLAs), operational performance, supplier scorecards, issue management, and continuous quality improvement.
Segment - Deployment
Revenue capture definition
Cloud
Revenue generated from subscription-based vendor risk management solutions delivered through public, private, or hybrid cloud environments. Revenue includes SaaS subscriptions, cloud hosting, implementation, upgrades, maintenance, technical support, and managed services.
On-premise
Revenue generated from perpetual licenses, maintenance, implementation, upgrades, and support services for vendor risk management software deployed within an organization's own IT infrastructure and managed internally.
Segment - Enterprise Size
Revenue capture definition
Large Enterprises
The large enterprises segment, with respect to the number of employees, typically comprises organizations employing more than 1,000 employees for multinational corporations.
Small and Medium Enterprises (SMEs)
The SMEs segment, with respect to the number of employees, generally includes organizations employing between 10 and 999 employees.
Segment - End Use
Revenue capture definition
BFSI
Revenue generated from vendor risk management solutions used by banks, financial institutions, insurance companies, and fintech firms to manage third-party cybersecurity, operational, financial, and regulatory risks.
IT & Telecom
Revenue generated from software used to assess and continuously monitor technology vendors, cloud service providers, software suppliers, and telecommunications partners for security, compliance, and operational performance.
Retail & Consumer Goods
Revenue generated from vendor risk management platforms that monitor suppliers, logistics providers, manufacturers, and service vendors to ensure supply chain resilience, compliance, and operational continuity.
Manufacturing
Revenue generated from solutions that manage supplier risk, procurement compliance, operational resilience, product quality, and third-party performance across manufacturing value chains.
Energy & Utilities
Revenue generated from platforms that assess vendor cybersecurity, infrastructure resilience, regulatory compliance, and operational risks for utilities, oil & gas, renewable energy, and power generation organizations.
Healthcare
Revenue generated from vendor risk management solutions used by healthcare providers, pharmaceutical companies, and life sciences organizations to evaluate third-party compliance, cybersecurity, patient data protection, and supplier reliability.
Government
Revenue generated from solutions deployed by government agencies and public-sector organizations to assess contractor risks, procurement compliance, cybersecurity posture, and regulatory adherence across third-party vendors.
Others
Revenue generated from vendor risk management software adopted across sectors such as education, transportation, logistics, hospitality, media, real estate, and professional services to strengthen third-party governance and risk management.
Estimation Model
Layer
Question
Analysis
Third-Party Risk & Regulatory Demand Layer
Who can benefit from vendor risk management software?
Identify organizations that engage with third-party vendors, suppliers, contractors, cloud service providers, and outsourcing partners and must manage operational, cybersecurity, financial, compliance, and reputational risks. These include enterprises across BFSI, healthcare, manufacturing, retail, IT & telecommunications, energy & utilities, government, and other industries. Organizations seeking to strengthen third-party governance, automate vendor due diligence, ensure regulatory compliance, improve supply chain resilience, and reduce vendor-related risks represent the core demand base for vendor risk management software.
Digital Transformation & Risk Management Readiness Layer
Who can deploy vendor risk management software?
Evaluate organizations based on their procurement maturity, digital transformation initiatives, cloud adoption, governance, risk, and compliance (GRC) frameworks, cybersecurity programs, supplier management processes, and enterprise application landscape. Organizations operating integrated procurement, ERP, cybersecurity, and compliance environments with structured vendor governance processes possess the operational readiness to successfully deploy vendor risk management software.
Adoption & Utilization Layer
Who actively uses vendor risk management software?
Analyze software adoption across multinational enterprises, financial institutions, healthcare organizations, manufacturers, retailers, technology providers, government agencies, and critical infrastructure operators that manage extensive third-party ecosystems. Active users leverage vendor risk management software for vendor onboarding, due diligence, cybersecurity assessments, financial risk evaluation, compliance monitoring, contract oversight, continuous vendor monitoring, audit management, risk scoring, remediation tracking, and enterprise-wide third-party risk governance.
Monetization Layer
How much revenue is generated?
Assess revenue generated through subscription-based (SaaS) and perpetual licensing of vendor risk management software, including modules for vendor information management, contract management, financial controls, compliance management, audit management, quality assurance, risk assessments, continuous monitoring, analytics, dashboards, and reporting. Additional revenue streams include implementation, customization, system integration, consulting, managed services, employee training, technical support, software maintenance, upgrades, and long-term enterprise subscription and professional service agreements associated with vendor risk management deployments.
Delivered Customizations
This report has been delivered with the following In-depth customizations
Client Request
Customization Delivered
Value Adds
AI-Driven Vendor Risk Intelligence & Automation Trends
Conducted a structured analysis of AI-powered vendor risk management technologies, including automated vendor due diligence, continuous risk monitoring, predictive risk analytics, cybersecurity risk scoring, workflow automation, and intelligent third-party risk assessments.
Helps stakeholders understand emerging AI-enabled vendor risk technologies, identify innovation opportunities, and evaluate investments in automated third-party risk management and decision-making.
Cloud-Based Vendor Risk Management & Third-Party Monitoring Trends
Conducted a comprehensive analysis of vendor risk management adoption across public cloud, private cloud, hybrid, and multi-cloud environments, including SaaS-based VRM platforms, continuous vendor monitoring, cloud supplier governance, and integrated GRC ecosystems.
Conducted a comprehensive analysis of vendor risk management adoption across public cloud, private cloud, hybrid, and multi-cloud environments, including SaaS-based VRM platforms, continuous vendor monitoring, cloud supplier governance, and integrated GRC ecosystems.
Global Regulatory Compliance & Third-Party Risk Trends
Conducted a comprehensive analysis of vendor risk management solutions supporting regulations and frameworks such as DORA, NIS2, GDPR, HIPAA, PCI DSS, SOX, ISO 27001, and other third-party risk and cybersecurity compliance requirements, with emphasis on automated compliance workflows, continuous assessments, audit readiness, and regulatory reporting.
Helps stakeholders understand evolving third-party risk regulations, strengthen compliance strategies, mitigate cybersecurity and operational risks, and identify growth opportunities driven by expanding regulatory oversight and supply chain governance initiatives.
Frequently Asked Questions About This Report
The global vendor risk management market size was valued at USD 12.3 billion in 2025 and is estimated at USD 14.2 billion in 2026.
The global vendor risk management market is expected to grow at a compound annual growth rate of 15.2% from 2026 to 2033, reaching USD 38.1 billion by 2033.
The financial control segment led with a 32.7% revenue share in 2025, while the compliance management segment is the fastest-growing segment.
The on-premise segment led with a 65.7% revenue share in 2025, and cloud segment is second fastest growing market
The BFSI segment held the largest share of 27.4% in 2025. Digital transformation initiatives are driving growth in the VRM market for the BFSI segment.
Key players operating in the vendor risk management market include BitSight Technologies; Genpact; LogicGate; MetricStream, Inc.; NAVEX Global, Inc.; Prevalent, Inc.; ProcessUnity; Quantivate, LLC; SAI Global; ServiceNow
Key factors include organizations increasingly strengthening third-party risk oversight amid expanding digital ecosystems, globalized supply chains, and evolving cybersecurity threats
North America dominated with 59.0% revenue share in 2025.
Asia Pacific is the fastest-growing region over the forecast period.
About the Author(s)
IT Services & Applications Research Team
Technology · IT Services & ApplicationsThis report was authored by the it services & applications research team at Grand View Research - comprising two research analysts, one senior research analyst, and one industry expert - with specialized expertise in the it services & applications segment of the technology industry. All findings are based on proprietary technology databases, executive interviews, and regulatory analysis, subject to internal peer review prior to publication.
Last Updated:
Speak to Analyst

Customize this report to your needs - add regions, segments, or data points, with 20% free customization.
Or view our licence options:


ISO 9001:2015 & 27001:2022 Certified
We are GDPR and CCPA compliant! Your transaction & personal information is safe and secure. For more details, please read our privacy policy.


